Automate User Access Provisioning and Deprovisioning Across Your SaaS Stack

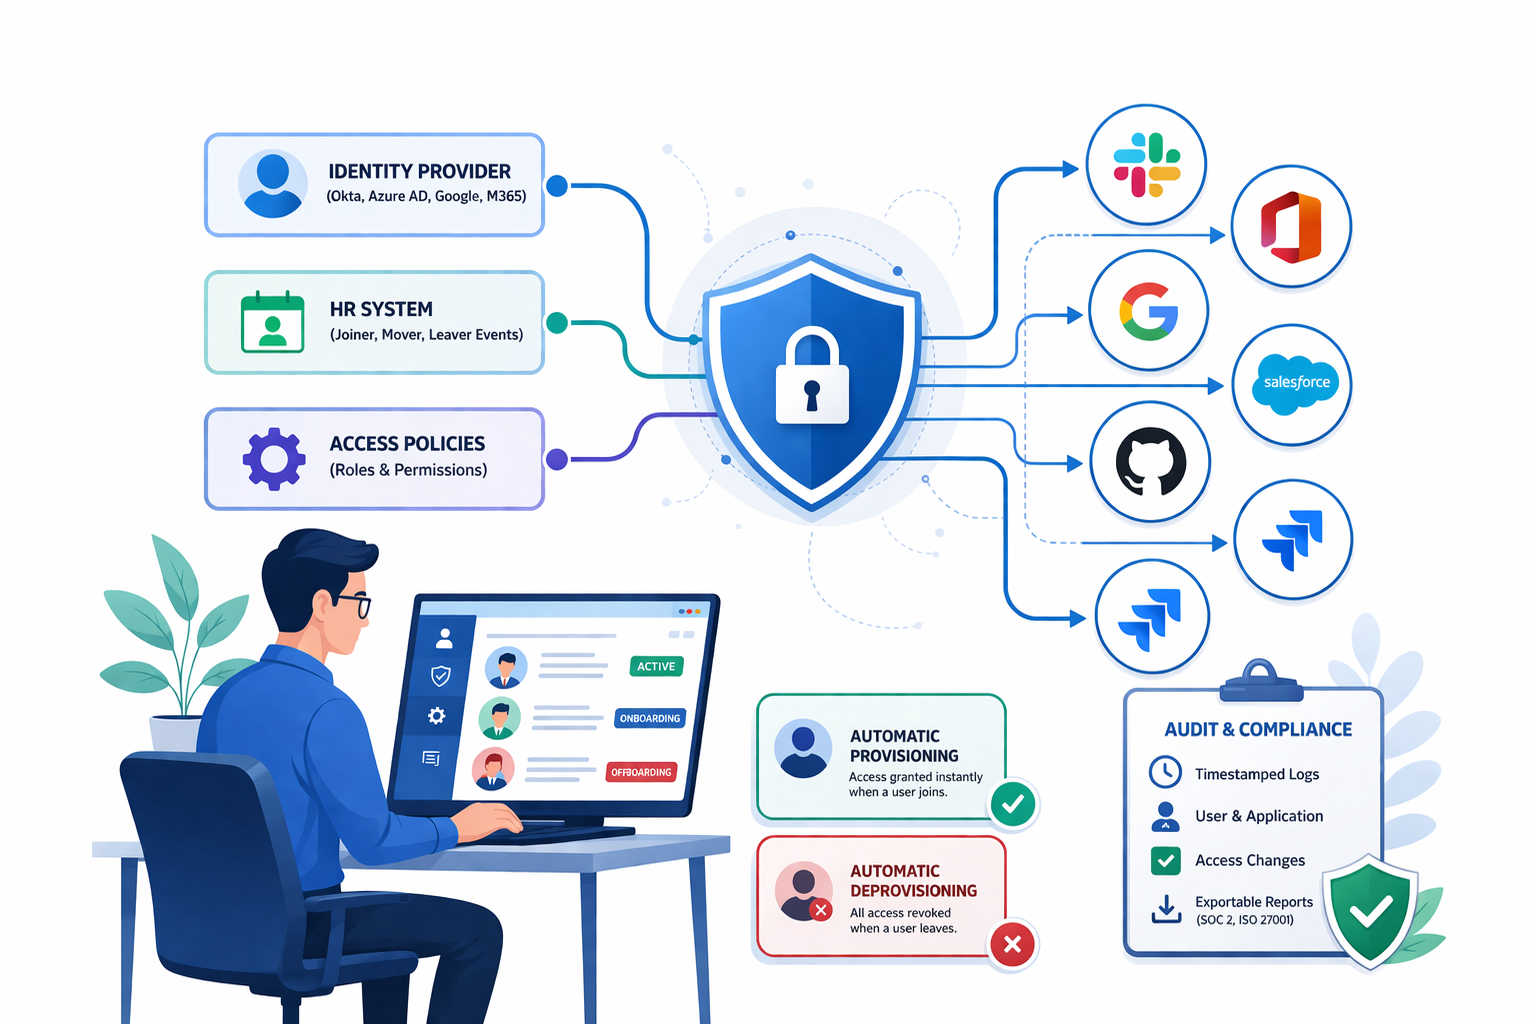
Provision the right access when a user joins. Revoke everything when they leave. CloudNuro eliminates manual tickets, prevents orphaned accounts, and maintains audit-ready records of access changes.

Built for IT and security teams. CloudNuro uses HR and identity events to trigger provisioning and deprovisioning workflows across connected SaaS systems.
10x
Faster Employee Provisioning
100%
AccessRevoked on User Exit
Zero
Orphaned Accounts

Why Manual SaaS Access Control Keeps Creating Risk

Manual user provisioning and deprovisioning produces the same security, compliance and productivity failures every time.

Delayed Access Provisioning

Provisioning delays leave new hires without critical tools and slow productivity from day one.

No Centralised Access Governance

Lack of centralized visibility creates access blind spots across SaaS applications and users.

Overprovisioned Access Violates Least Privilege

Excess permissions increase security risks and weaken compliance across critical SaaS systems.

Orphaned Accounts Create Security Exposure

Former employees retaining access create orphaned accounts and increase unauthorized access risk.

No Audit-Ready Access Logs

Scattered access records make audits difficult and reduce visibility into user activity history.

Unused Licenses Drain SaaS Budget

Inactive accounts continue consuming SaaS licenses and quietly increase unnecessary software spend.

How CloudNuro User Access Work

→
↓
Okta
Azure AD
Joiner Mover Leaver
Step 1
Connect Your Identity
Provider and HR System
Visual Policy Builder
Role-Based
Least Privilege
Approval Gates
✓ Set Once Every JML Event
Step 2
Define Access Policies
and Workflows
⚙️
📊
📁
🔗
Access Provisioned
Session Terminated
Step 3
Automatically Provision
and Deprovision Access

Key Capabilities

End-to-end identity lifecycle management across every joiner, mover and leaver event.

Provisioning

  • Pre-join trigger with configurable timing
  • IDP account creation (Okta, Azure AD, Google Workspace, Microsoft 365)
  • Role-based access provisioning with least privilege enforcement
  • JML lifecycle workflow support (Joiner, Mover, Leaver)
  • SaaS app provisioning across 50-plus integrations
  • Per-app approval logic (auto or admin-approve)
  • HRMS-triggered automatic workflow launch
  • Step-level monitoring and real-time failure alerts
  • Notifications via email, Slack, and Microsoft Teams

Deprovisioning

  • Immediate access revocation across all SaaS apps
  • Active session termination for supported applications
  • Automated email forwarding and out-of-office setup
  • File and resource transfer to nominated successors
  • License reclamation workflows for supported applications
  • Audit-safe IDP account suspension
  • Exportable audit logs for SOC 2 and ISO 27001
  • Centralized deprovisioning workflow visibility
  • Step-level execution tracking for offboarding

Works With the Tools Your Team Already Uses

HR systems trigger events. Identity providers and CloudNuro enforce access.

Why Forward-Thinking IT Teams Choose CloudNuro

Purpose-built for enterprise IT teams who need complete control over User access
Scroll to compare all columns
Capability
✕Manual
−Generic Tool
✓CloudNuro
Best Choice
IDP integration depth None Basic SCIM Full: Okta, Azure AD, Google, M365
Role-based access provisioning No Partial Yes, from day one
Least privilege enforcement No No Yes, built into every workflow
JML lifecycle support No Partial Yes, Joiner, Mover, Leaver
Real-time deprovisioning No Delayed Yes, immediate on leaver detection
Session termination No No Yes, across all apps simultaneously
License reclamation No No Yes, automatic
Exportable audit logs No Limited Yes, SOC 2 and ISO 27001 ready

Frequently Asked Questions

Does this work for contractors, vendors, and temporary workers - not just full-time employees?

How long does implementation take?

Can multiple users be provisioned simultaneously?

Who in our organisation should own and manage the workflows?

What happens to app licenses when access is revoked during offboarding?

Is there role-based access control within CloudNuro itself?

How is least privilege access enforced?

How are mover events handled?

Does CloudNuro support access reviews for compliance audits?

Can workflows be customized per department?

Customer Reviews

Last year, we spent about $2.3 million on SaaS, and CloudNuro helped us uncover $450,000 in potential savings, along with $53,000 in cost avoidance and $44,000 in operational efficiency. What stood out to me was having the data to clearly see these opportunities.
Anthony L. McPhearson
CIO
Review Image

CloudNuro sees what browser tools miss. It's the AI visibility layer that captures agentic workflows, mobile usage, and browser extensions - giving you the full picture of what AI is actually running in the wild. Three streams, one complete view.

Manny Singh
CISO
Review Image
Arrow
Arrow

Build the Foundation for SaaS Governance

Sign up for CloudNuro.ai today and experience the difference firsthand.

Connect up to three SaaS apps for free, see actionable insights in 24 hours.